For fifteen years, bank model risk management meant credit, market and capital models: documented, validated and reviewed on a cycle. Machine learning stretched that discipline. Generative AI and AI agents break parts of it, because their outputs vary, they are often supplied by a third party, and they change when the vendor updates them. Regulators have noticed. Between November 2025 and September 2026, supervisors in Australia, Singapore, Hong Kong, the UAE and the United States each published new expectations on AI risk. None has yet written a binding AI prudential standard, but their messages converge on the same handful of controls. This article sets out what each regulator has said, where they agree, and how to build a model risk programme that will satisfy all of them.
APRA's April 2026 letter: a step-change is required
On 30 April 2026, APRA wrote to all regulated entities after a targeted review of large banks, insurers and superannuation trustees. Its letter on artificial intelligence calls for a step-change, because governance, risk management, assurance and resilience are not keeping pace with adoption. Its main findings:
- Boards are still building the technical literacy to challenge AI risk, and rely too much on vendor presentations.
- Lifecycle controls are weak after deployment. Few entities continuously validate models for drift, bias or failure, and APRA says point-in-time, sample-based assurance is ill suited to probabilistic models.
- Cyber and identity controls have not adjusted to non-human actors such as AI agents, and staff use of AI tools outside approved controls relies on policy rather than technical prevention.
- Third parties are concentrated. Exit plans are rarely tested, and contracts often lack audit rights and model-update or incident notification clauses. APRA expects entities to map the full AI supply chain, including foundation model providers as fourth parties.
APRA is not proposing new requirements at this stage. It expects existing prudential standards to be met and has said it will take stronger supervisory action where AI risk is poorly managed. In practice that means AI now sits inside CPS 230 operational risk and CPS 234 information security reviews.
What each regulator has said
| Regulator | Instrument | Status in September 2026 | Key expectations |
|---|---|---|---|
| APRA (Australia) | Letter to industry on AI, 30 April 2026 | Supervisory expectations under existing standards | Board AI literacy, AI inventory, lifecycle ownership, continuous validation, AI supply chain mapping |
| MAS (Singapore) | Consultation paper on Guidelines on AI Risk Management, 13 November 2025 | Not yet final; MAS said in August 2026 they will be finalised soon, with a proposed 12-month transition | All AI including GenAI and agents; AI inventory; materiality assessment by impact, complexity and reliance |
| BNM (Malaysia) | Discussion paper on AI, August 2025; revised RMiT, in effect 28 November 2025 | No AI-specific policy document yet | Board accountability for technology risk; assessment, testing and monitoring before deploying new technology |
| HKMA (Hong Kong) | GenAI consumer protection circular, August 2024; AI-enabled cyber threats circular, mid-2026 | In force as supervisory guidance | Validation, fairness, customer opt-out from GenAI, defences against AI-enabled attacks |
| CBUAE (UAE) | Guidance note on responsible adoption of AI and ML, February 2026 | Non-binding guidance | AI model inventory, bias stress testing, three oversight models, human review rights for consumers |
| SAMA (Saudi Arabia) | No AI-specific banking guidance found | SDAIA AI Ethics Principles (2023) and SAMA's cyber framework apply | Map AI use to existing SAMA and NCA controls |
| US Fed, OCC and FDIC | SR 26-2, 17 April 2026, replacing SR 11-7 | Non-enforceable guidance for banks above US$30bn | Inventory, effective challenge, validation, vendor models; GenAI and agentic AI excluded for now |
Two points stand out. First, Singapore's guidelines are still a consultation, so no effective date should be assumed. Second, the new US guidance deliberately leaves generative and agentic AI out of scope while the agencies consult further, which means the Asian and Gulf regulators are, for once, ahead of Washington on the hardest part of the problem.
Where regulators agree
Read side by side, the documents share five expectations. They are the backbone of any AI model risk programme in the region.
- A complete AI inventory. APRA, MAS, the CBUAE and SR 26-2 all require one, covering in-house models, vendor models and AI embedded in purchased software.
- Risk-tiering. Controls proportionate to materiality. MAS proposes impact, complexity and reliance as the dimensions; the CBUAE allows fully automated decisions only for low-risk, non-material processes.
- Validation that continues after launch. Pre-deployment testing is no longer enough. Drift, bias and failure monitoring must run while the model is in use.
- Human oversight matched to risk. Human involvement for high-risk decisions, and a route for customers to seek human review.
- Third-party accountability. Outsourcing a model does not outsource the risk. Contracts, testing rights and exit plans must cover AI providers, including the foundation model behind a vendor product.
The DFSA's 2025 AI survey of firms in the DIFC found that 52% used AI, up from 33% a year earlier, and 21% lacked clear accountability or oversight for it. The gap between adoption and governance is what every regulator above is trying to close.
Why classic model validation struggles with generative AI
Traditional validation tests conceptual soundness, benchmarks outcomes and monitors performance against a stable model. Generative AI challenges each step. Outputs vary for the same input. The model may be a vendor service that changes without notice. There is often no clean ground truth to measure against. In a September 2026 speech, the chair of the BIS Financial Stability Institute said model risk expectations built for transparent statistical models must be revisited for large language models.
Until that happens, banks are adapting with practical measures:
- Scenario and red-team testing of prompts, including prompt injection and data leakage attempts.
- Output sampling and scoring in production, with thresholds that trigger review.
- Version pinning and change notice clauses, so a vendor model update is treated as a model change.
- Guardrails and fallbacks for any AI that supports a critical operation, so the service continues if the model is withdrawn.
Fraud is where the risk is most visible. In early 2024, an employee in engineering firm Arup's Hong Kong office joined a video call with deepfaked senior colleagues and made transfers totalling about HK$200 million, as CNN reported. Payment approval controls now need to assume that voices and faces can be faked.
A practical AI model risk framework
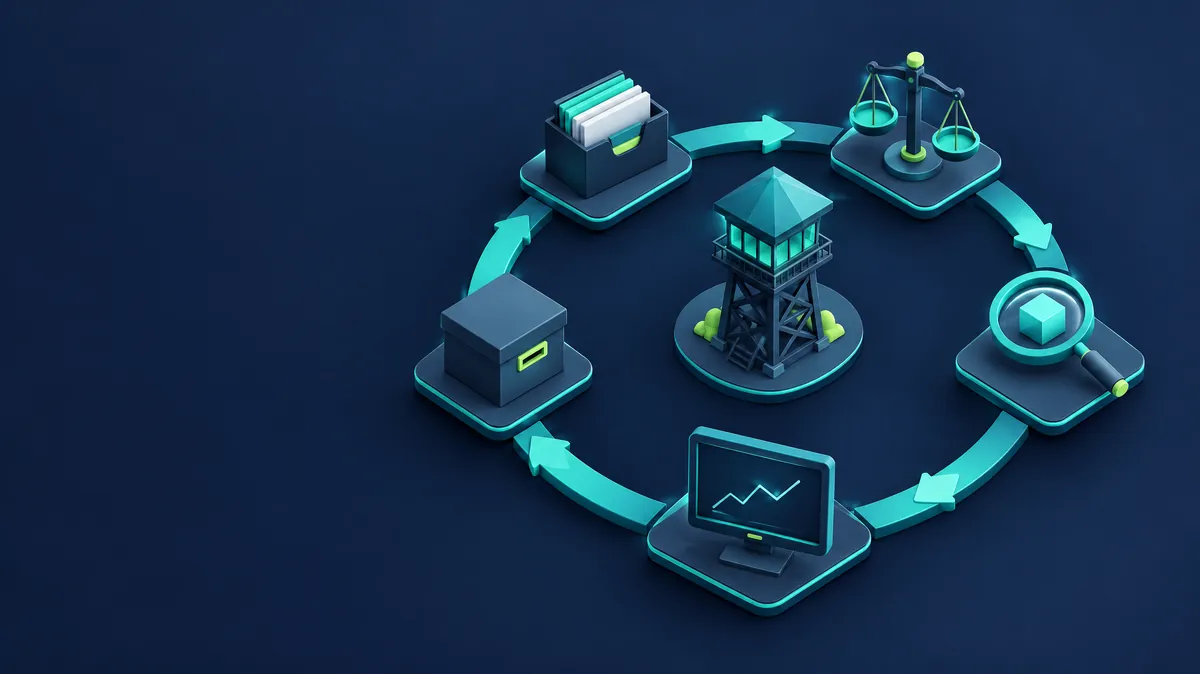
| Stage | Control | Evidence a supervisor will ask for |
|---|---|---|
| Inventory | Register every AI use case, model and vendor dependency | Current register with owner, purpose, provider and risk tier |
| Tiering | Rate each use case by impact, complexity and reliance | Documented materiality assessment and approval |
| Pre-deployment | Validation, bias testing, security testing, legal and privacy review | Validation report, test results, sign-offs |
| In production | Drift, bias and output monitoring; incident logging | Monitoring dashboards, threshold breaches and actions |
| Change | Treat vendor and prompt changes as model changes | Change tickets and revalidation records |
| Retirement | Decommission and remove access | Decommission record and archived documentation |
This lifecycle maps onto ISO/IEC 42001, which gives the management system a certifiable structure. For the governance picture beyond banking, see our guides to AI governance in Australia and New Zealand, AI governance in Saudi Arabia, the UAE and Pakistan, and governing AI agents under ISO/IEC 42001.
Running AI model risk in GRCLens
GRCLens holds the AI inventory as a register linked to risks, controls and suppliers, so a vendor model appears both in the model register and in third-party risk. Materiality assessments, validation reports and monitoring evidence are attached to each model with their dates, and the same records map to APRA prudential standards, MAS TRM, BNM RMiT and ISO/IEC 42001. Because GRCLens can run inside your own infrastructure, with its AI evidence review hosted locally, model documentation never leaves the bank's environment.
Frequently asked questions
Has APRA issued an AI prudential standard?
No. APRA's 30 April 2026 letter sets expectations under existing standards such as CPS 230 and CPS 234, and APRA said it is not proposing additional requirements at this stage.
Are the MAS AI Risk Management Guidelines final?
Not as of late September 2026. MAS consulted from November 2025 to January 2026 and said in August 2026 the guidelines would be finalised soon, with a proposed 12-month transition after issuance.
Does SR 26-2 cover generative AI?
No. The April 2026 US guidance applies to traditional models and non-generative AI. The agencies said they will consult separately on generative and agentic AI.
What is the first step in AI model risk management?
A complete inventory of AI use, including models embedded in vendor software. Every regulator above expects one, and every other control depends on it.
How Security Solution Consultants can help
Security Solution Consultants helps banks, insurers and financial institutions build AI inventories, risk-tiering methods and validation programmes that meet APRA, MAS, BNM and Gulf expectations. See our compliance and risk management advisory and our AI governance guide for businesses. For the security testing side, read securing AI solutions. GRCLens then keeps the inventory, assessments and monitoring evidence current. Request a demonstration.
Keep reading
Governing AI Agents Under ISO/IEC 42001: Registers, Impact Assessments and Evidence
ISO/IEC 42001 was published before most organisations ran AI agents, but its structure fits them well. How to extend an AI management system to agents: the register, the impact assessment trigger, the life cycle controls and the evidence.
AI Governance in Australia and NZ: 2026 Guide
Australia and New Zealand chose existing laws over an AI Act. What is mandatory, what is voluntary, and what starts in December 2026.
AI Governance in Saudi, UAE and Pakistan 2026
Saudi Arabia, the UAE and Pakistan have no general AI law yet. Which AI rules bind you, which are voluntary, and where ISO 42001 fits.