
Our Products
The GRCLens platform: purpose-built software for multi-framework compliance, payment security and AI-assisted assurance.
Software that runs your compliance program
One platform, modular by entitlement: enable exactly the frameworks and suites each organization needs.
Buying for a bank, insurer or government agency? Our checklist of GRC platform requirements for regulated entities covers the capabilities, contract clauses, SLAs and data residency commitments to ask for.
GRCLens Compliance Platform
The multi-tenant core: run NCA-ECC, PDPL, PK-CTDISR, ISO/IEC 27001, 20000-1, 42001 and SOC 2 side by side with shared evidence and live scoring.
- Control-by-control assessments
- Evidence repository with AI review
- Statement of Applicability
- Live dashboards & trends
PCI DSS Compliance Suite
A complete PCI DSS v4 workflow, from scoping and SAQ selection through gap analysis to ROC, AOC and acquirer submission.
- SAQ A–D & ROC workflows
- Gap analysis & remediation
- AOC generation & sign-off
- Send-to-acquirer packaging
Baseerah بصيرة · LensIQ
AI that reads your evidence: relevance and confidence analysis per control, executive posture summaries, and prioritised actions, always with a human in the loop.
- Evidence relevance scoring
- Executive AI summaries
- KPI/KRI intelligence
- Bilingual (English & Arabic)
Registers, SoA & Reporting
Dynamic registers (risk, AI systems, RoPA), point-in-time assessment history, and scheduled board-ready reports in PDF, Word or Excel.
- Risk heatmaps
- Version history & audit trail
- Scheduled report delivery
- PDF / Word / Excel export
One family of security platforms & services
GRCLens is part of the Security Solution Consultants family: explore our platforms and advisory services.
GRCLens.net
Multi-framework compliance platform: NCA-ECC, PDPL, PK-CTDISR, ISO and SOC 2 in one program.
Visit site ↗ ↗
EASMLens
External Attack Surface Management: continuous discovery and monitoring of your internet-facing assets.
Visit site ↗ ↗
NSPM
Network Security Policy Management: multi-vendor firewall governance: rule analysis, path and exposure risk, governed change with rollback, and segmentation evidence taken from the live rulebase.
Learn more → →
PhishLens
Phishing simulation and awareness testing: campaign engine, click and repeat-clicker analytics, and executive reporting.
Learn more → →Incident & Crisis Management
One record from incident to major incident to crisis: ISO 27035 and NIST 800-61r3 handling, ISO 22320 command, ISO 22361 board reporting and scored exercises.
Learn more → →Real screens from GRCLens
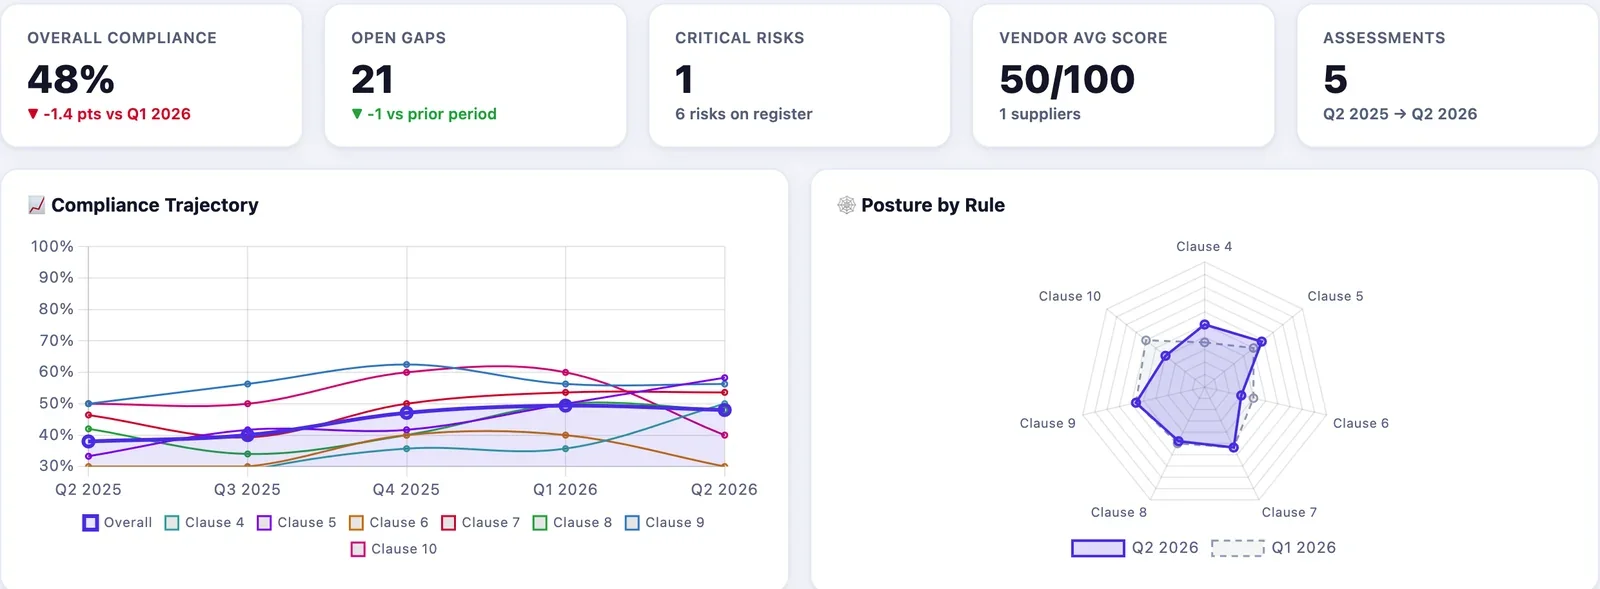
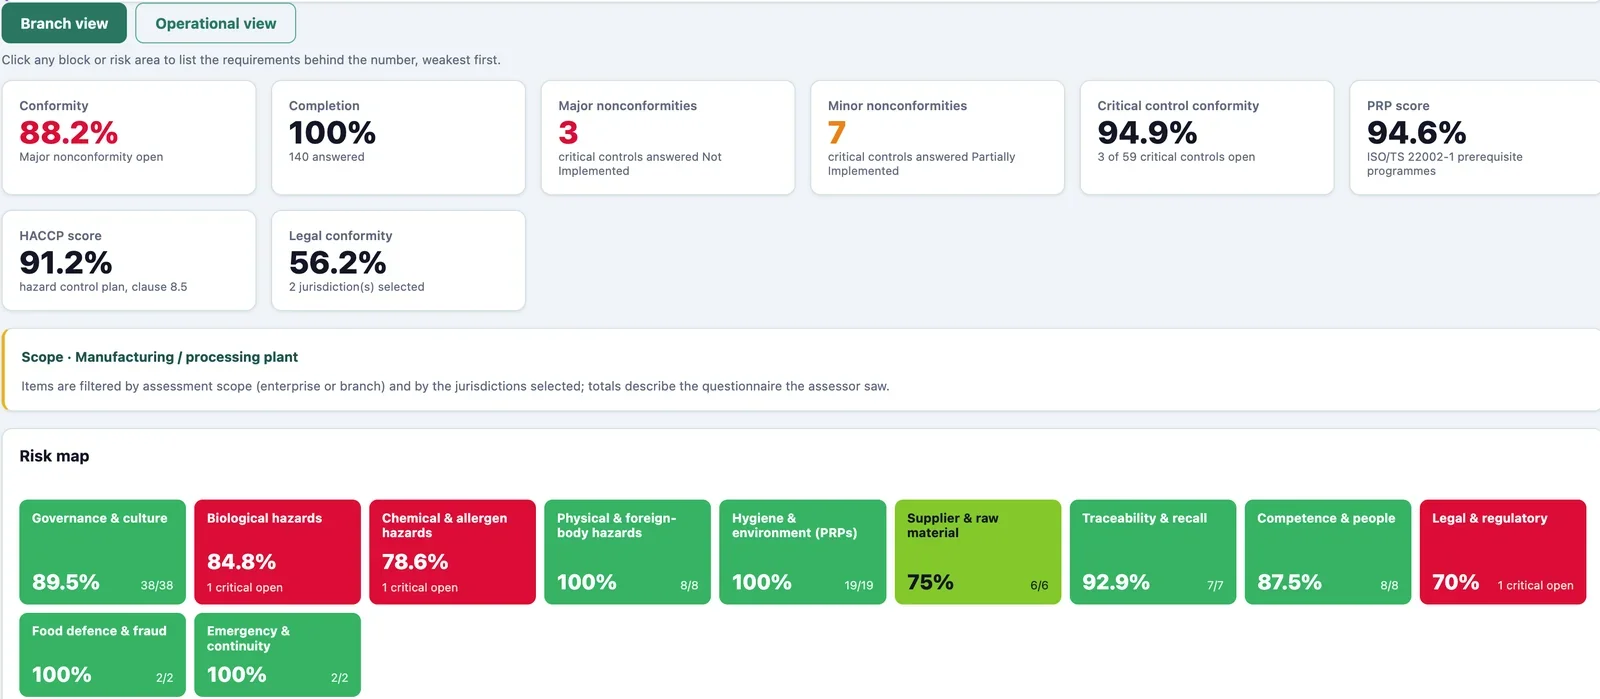
What boards, risk owners and assessors see: posture over time, scores by clause, and risk areas that lead straight to the requirements behind them.

See the platform live
Book a demo and we'll walk your team through the modules you need.