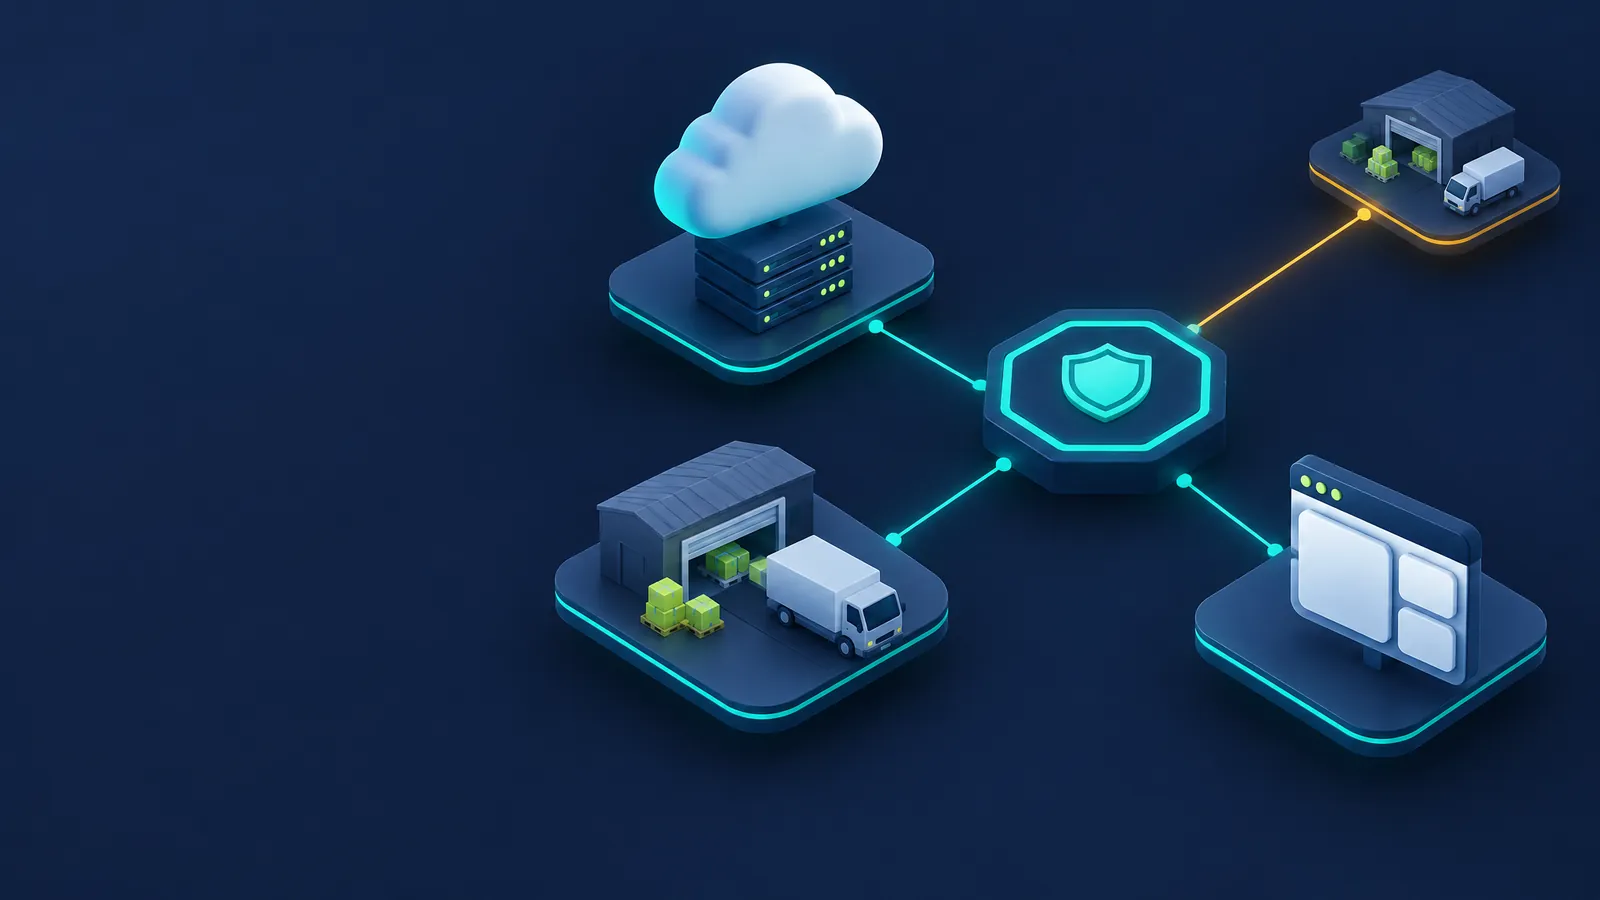
Outsourcing a service does not outsource the risk. Gulf frameworks consistently expect organizations to govern the security of their third parties and cloud platforms, and to evidence that oversight.
The expectation
NCA-ECC dedicates controls to third-party and cloud cybersecurity, and Dubai's ISR and the UAE IA Standards carry similar themes. The common thread: due diligence before engagement, security obligations written into contracts, and ongoing monitoring throughout the relationship.
Data residency and cross-border transfer rules under KSA and UAE privacy law add a further dimension when suppliers process personal data abroad.
A workable approach
Maintain a register of suppliers and sub-processors, classify them by the sensitivity of what they handle, and align assurance effort to that risk. High-risk providers warrant deeper review and stronger contractual controls.
Reusing assurance evidence (certifications, audit reports) reduces the burden on both sides while keeping the record defensible.
Bringing it together
Third-party risk sits at the intersection of cybersecurity and privacy. Managing it inside the same platform as your ECC and PDPL controls keeps the picture coherent and the evidence in one place.
Keep reading
GRC Platform Requirements for Regulated Entities: A Buyer's Checklist
A GRC platform holds your risk register, control weaknesses and incident records, and your regulator may treat its vendor as material. What to require from the product, the contract and the hosting before you sign.
One Supplier Assurance Programme for APRA CPS 230, MAS, HKMA, SAMA and the CBUAE
Third parties featured in 48% of breaches in Verizon's 2026 report, and regulators now want registers, audit rights, exit plans and concentration analysis. How to run one supplier assurance programme across Australia, Singapore, Hong Kong and the Gulf.
RMiT 2025 for Malaysian financial institutions: the 90-day clock, cloud, and the supplier you forgot
Bank Negara Malaysia's revised Risk Management in Technology took effect on 28 November 2025. What changed, why external-party assurance and cloud consultation are where most gaps sit, and how to keep the annual self-assessment honest.